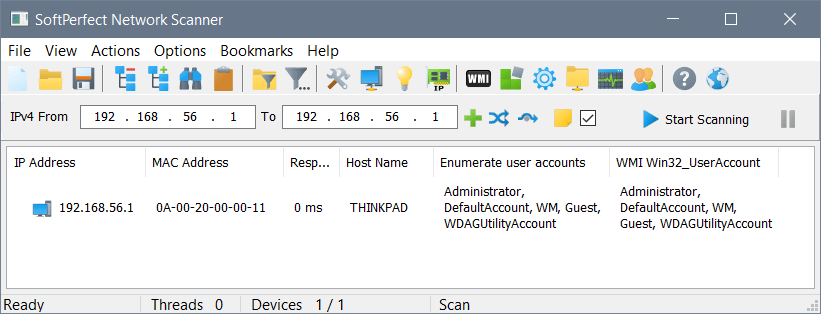
Technique used to enumerate remote user accounts
2 posts · Closed
There is an option inside the NetScan tool that allows us to enumerate user accounts on remote machines. It works fine, but the problem is that it only works for some machines and, for others, I don't know why it is not bringing the users. My question is: what is the technique used to gather these users on the local machine?
I tried to allow win32_UserAccount through WMI, but it isn't this technique that is used. I also thought this could be the same procedure applied by the Nmap script smbenumuser, but it looks like that isn't it either.
I'm a little bit lost because I would like to understand how it is performed in order to allow this on the machines where it isn't working. Can you guys give me some help here?
We use the NetUserEnum WinAPI function at level 0 to enumerate user accounts. If the function returned an error, nothing will be displayed.
This function should return a result similar to this WMI query:
SELECT Name FROM Win32_UserAccount
Here is what both retrieve on a local PC: